

AgentSec
Security for the agents doing the work
Agents sign in to your app with an identity they own, and call your APIs with only the tools you allow. One owner, one identity, one revoke switch.
- Agents sign in like users do
- The browser OIDC code flow with a key the agent owns. No shared secrets.
- Scope every tool call
- Allowed tools, scopes, and origins per agent.
- Cut off in one click
- New sign-ins and new tokens stop at once. Owners stay accountable.
Pick your plan
No credit card required. Change plans any time from Plan & Billing.
Authentication for agents
Agents sign in the way people do
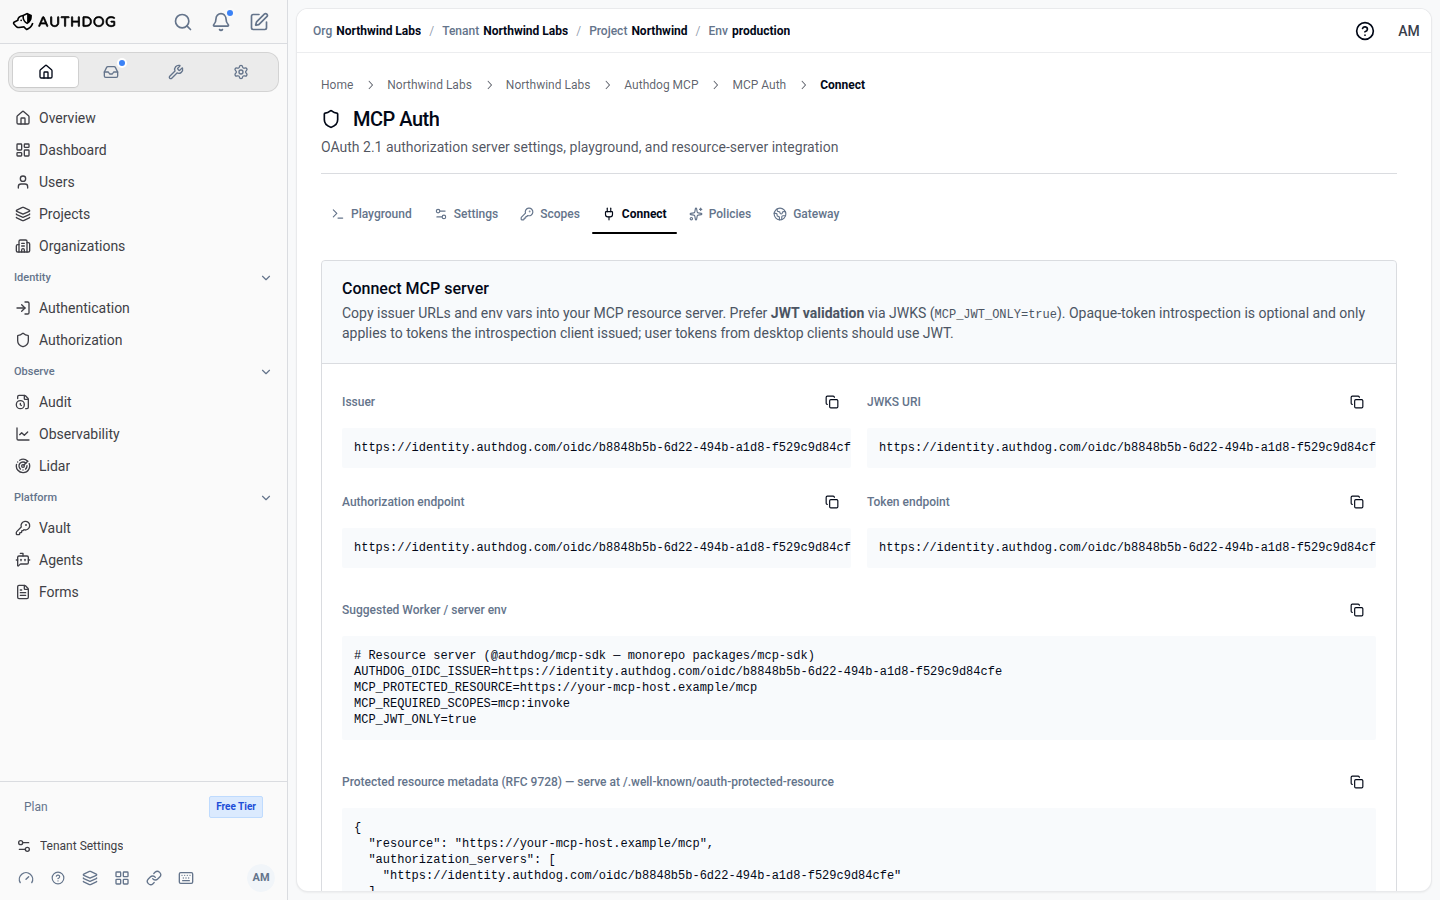
Agent Sign-In gives an agent what a person gets from your login page: an identity it owns, the standard OIDC code flow, and an owner who can cut it off. Add two config values to your app. No registration, no client secret.
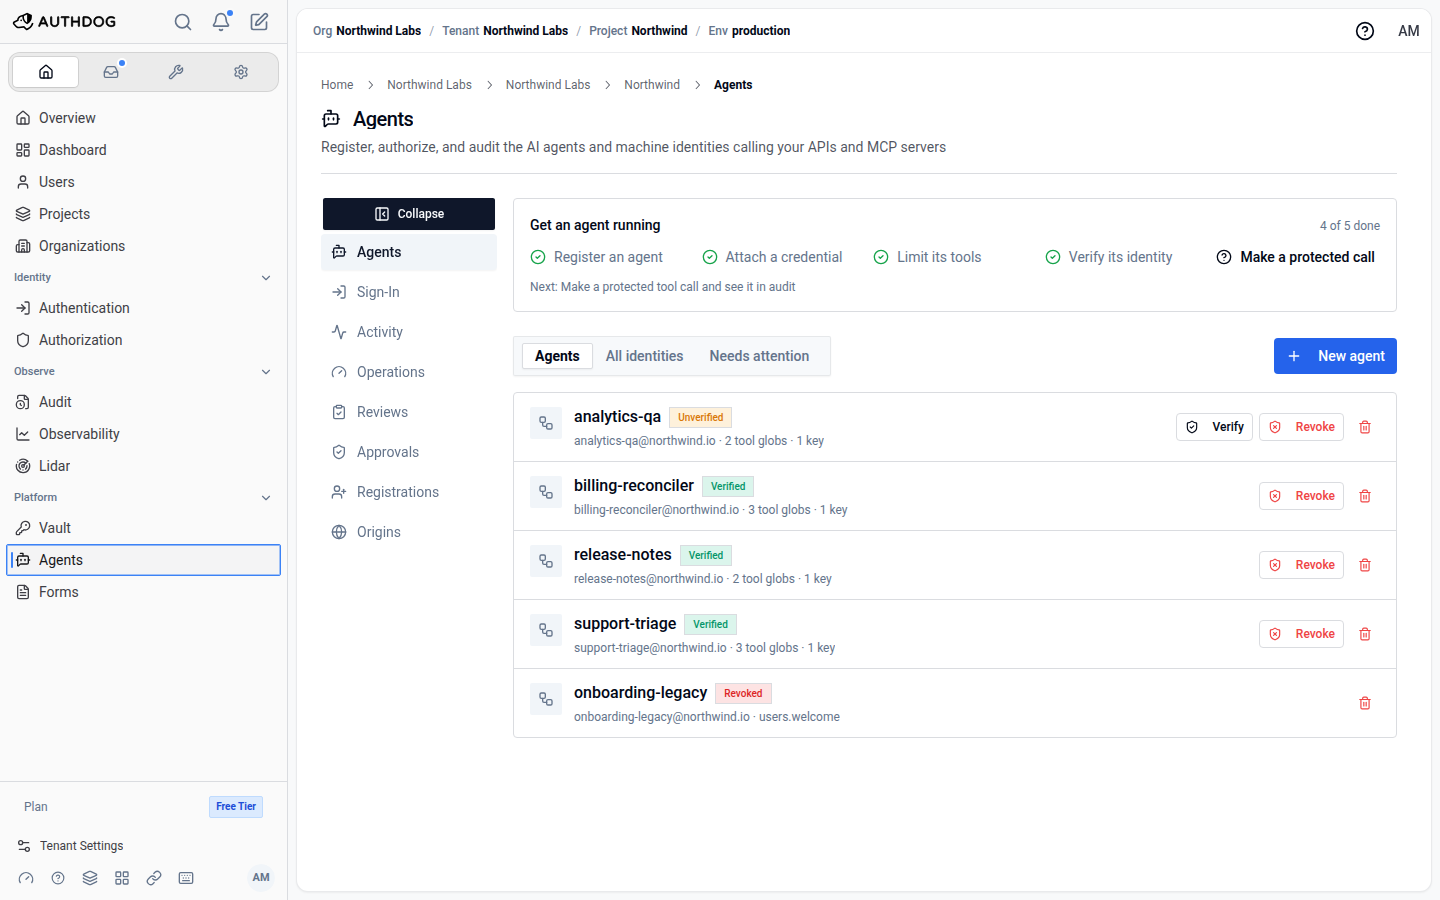
Two config values
Access control for agents
Every caller registered, scoped, and audited
Register every non-human caller in one place: a verified subject, allowed scopes, allowed tools, and a revoke switch. Approve what needs a person, review the rest.
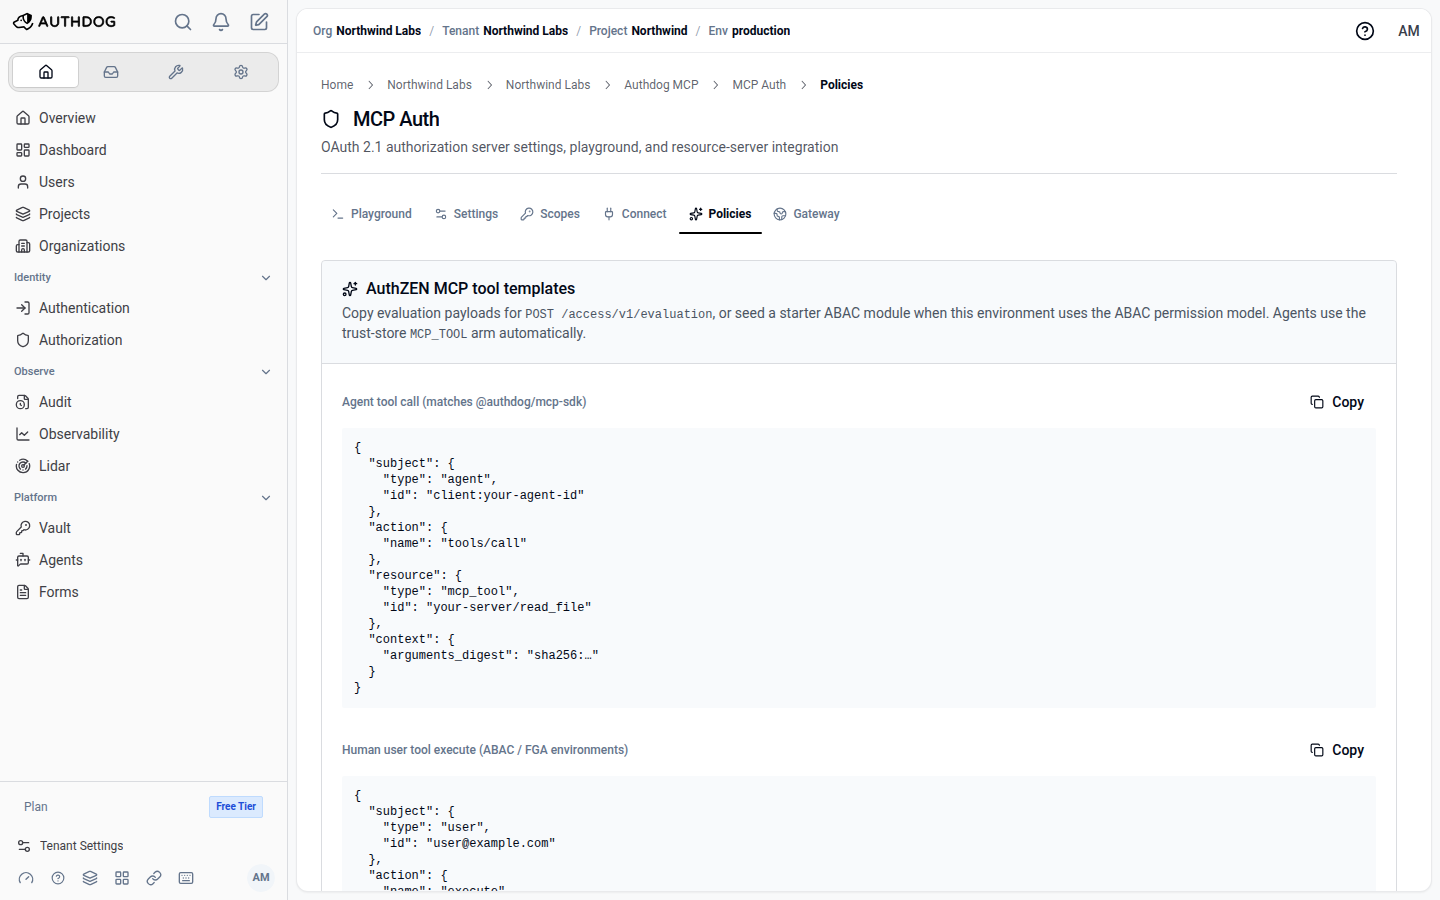
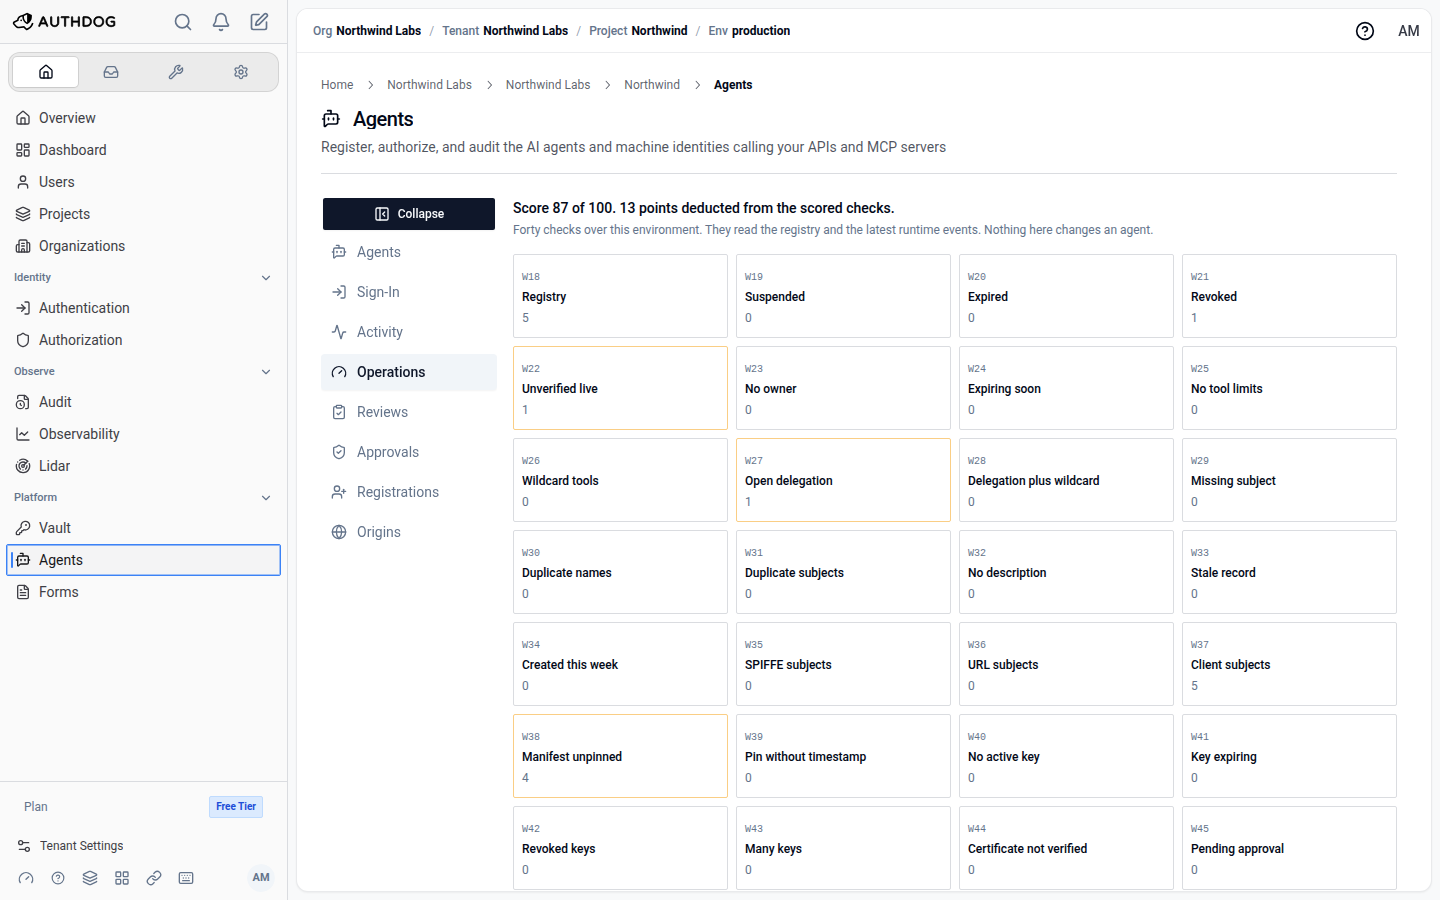
Register and verify
Lifecycle and detection
Delegation without impersonation, detection without guesswork
Agents acting on a user's behalf carry an explicit act chain, and Lidar watches the identity stream for the attacks that target them.
Token exchange, not impersonation
RFC 8693 delegation with a nested act chain and optional identity assertions — the resource always sees who is acting for whom.
Lidar threat detection
Monitors correlate agent-tool abuse, injection, and MCP rug-pulls on the same event stream as your human traffic.
One audit trail
Authentication events and tool activity land in the same environment audit log — actor type included.
How it works
Three steps to production
Integrate
Connect one SDK or API to your application.
Configure
Choose policies and capabilities for each environment.
Enforce
Ship globally with identity controls at the edge.
Free trial
Request a free trial
Tell us what you're building and we'll get you set up with a trial, plus someone who can answer questions as you evaluate.
- Full access to the platform while you evaluate it
- Help wiring it into your stack from someone who knows it
- Answers on SSO, SCIM, residency, and compliance requirements
Stop building a second product just to log people in.
Sign-in, access, and the audit trail — so you can get back to the actual app.