

Authdog MCP server
Run Authdog from your agent
The Authdog MCP server lets your agent set up projects, manage users, check your OIDC wiring, and more. No dashboard tab required.
MCP server
https://api.authdog.com/mcpclaude mcp add --transport http authdog https://api.authdog.com/mcpauthdog mcp install --client claude- Sign in, no key to paste
- Your agent signs in with OAuth. There is no API key to copy into a config.
- Server registry
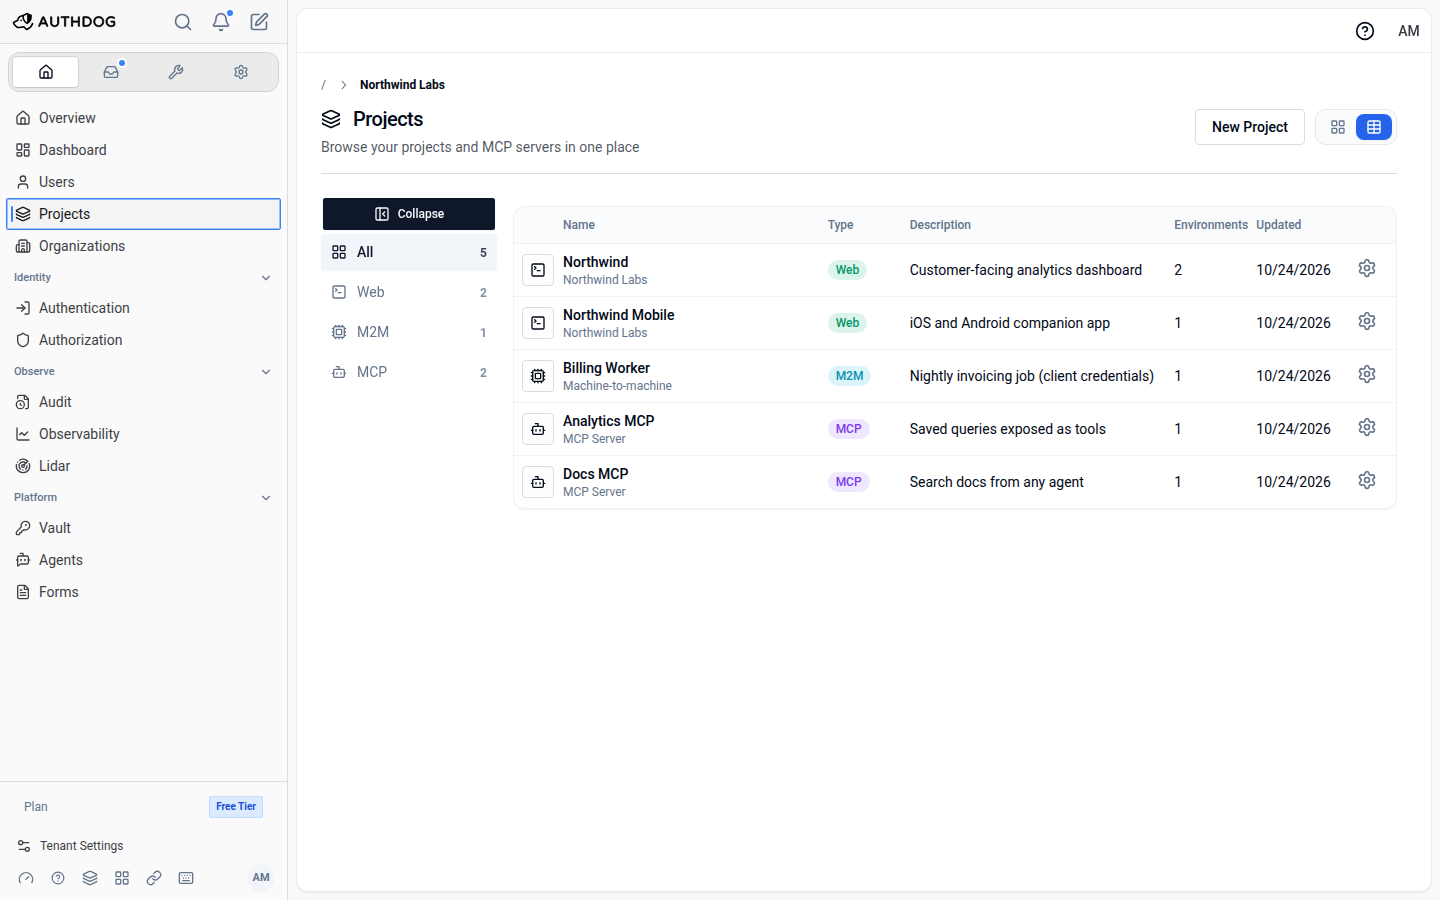
- Front your own MCP servers too: register each per environment with its transport and scopes.
- Scoped by design
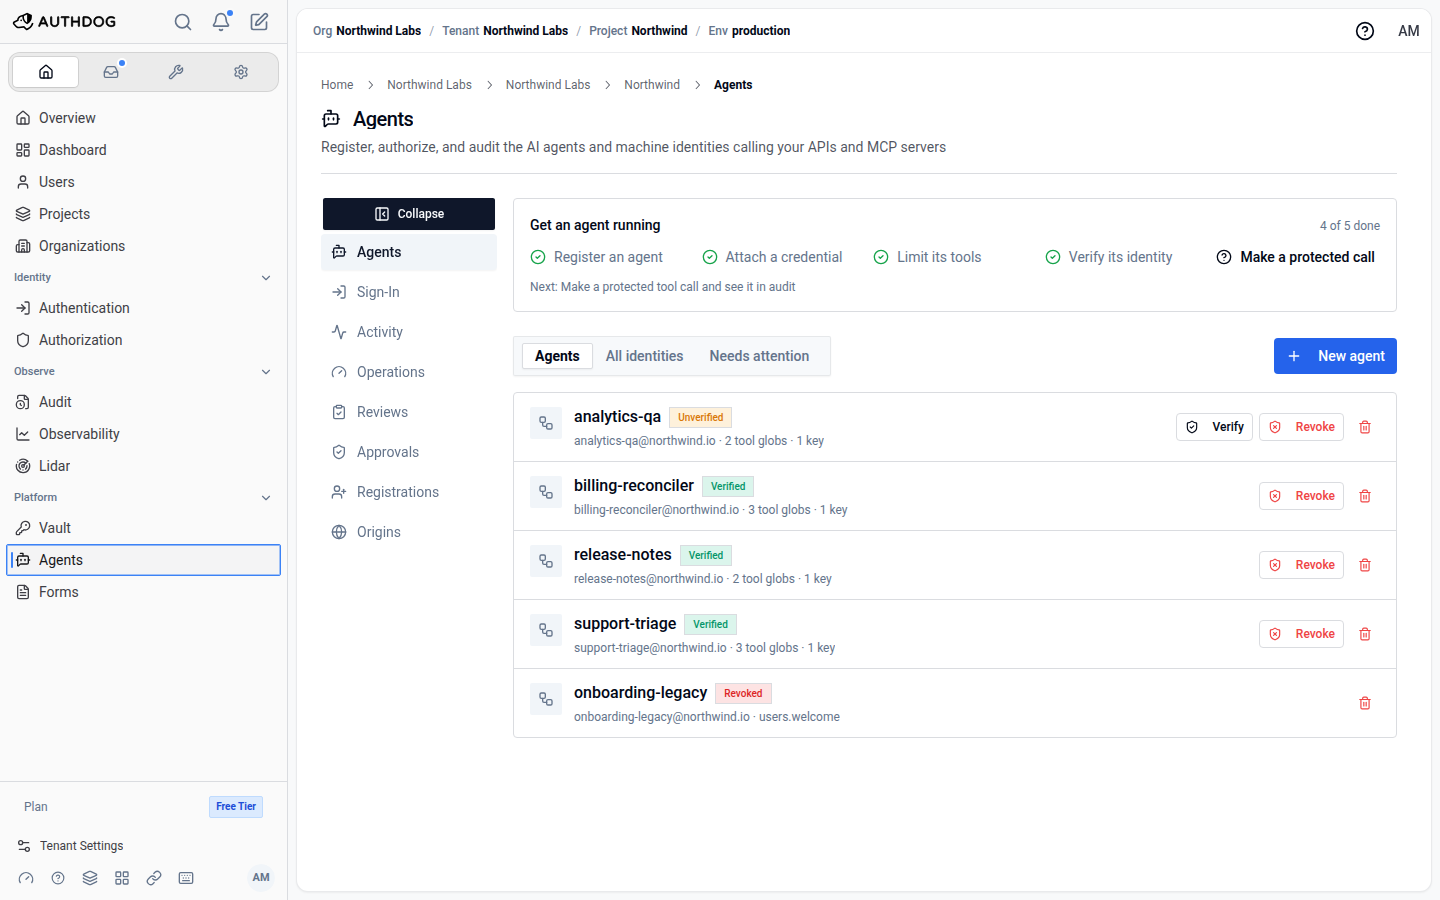
- Your agent gets only the tools and scopes its task needs.
- Every call on record
- The audit log shows who acted, which client, and whether it came from the console or an agent.
MCP SDK
Verify Authdog tokens inside your MCP server
The client sends its Authdog access token as a bearer token. The SDK verifier calls GET /v1/userinfo and hands your server an AuthInfo (subject, username, email, scopes, expiry). An invalid or expired token raises an authentication error your transport turns into a 401.
Verify an incoming bearer token and read the caller's identity.
import { AuthdogVerifier, AuthenticationError, APIError } from '@authdog/mcp-sdk';

// Initialize the verifier
const verifier = new AuthdogVerifier({
  baseUrl: 'https://api.authdog.com',
  timeout: 10000, // Optional, defaults to 10 seconds
});

// Verify an incoming bearer token
try {
  const authInfo = await verifier.verifyToken('the-access-token');
  console.log(`Subject: ${authInfo.subject}`);
  console.log(`Username: ${authInfo.username}`);
  console.log(`Email: ${authInfo.email}`);
  console.log(`Scopes: ${authInfo.scopes.join(', ')}`);
  console.log(`Expires at: ${authInfo.expiresAt?.toISOString() ?? 'unknown'}`);
} catch (error) {
  if (error instanceof AuthenticationError) {
    console.error('Authentication failed:', error.message);
  } else if (error instanceof APIError) {
    console.error('API error:', error.message);
  } else {
    console.error('Unexpected error:', error);
  }
}- 01
Install
Add the SDK for your server's language.
- 02
Verify
Pass the incoming bearer token to AuthdogVerifier, pointed at your Authdog API base URL.
- 03
Authorize
Use the returned AuthInfo to allow or deny each tool and resource call.
All SDKs live in authdog/mcp-sdk. They are source-available and registry publication is not confirmed, so installs may fail until release. Scopes are empty today because userinfo does not return them yet. For the Node runtime guard with trust store, AuthZEN, and telemetry, and per-language guides, see the MCP SDK docs.
Prompts
Ask your agent to set up, debug, and ship
Copy a task into any agent connected to the Authdog MCP server.
Set up
“Create a project for my storefront and give me the environment values for Next.js.”
create_projectget_environment_setupget_sdk_configDebug sign-in
“Figure out why ada@example.com can't sign in and tell me how to fix it.”
search_usersget_usertest_oidc_configurationRedirect URIs
“Check that https://app.example.com/callback is allowed, and add it to staging if it is not.”
validate_redirect_uriset_environment_redirect_urisLock out an account
“Suspend the account for ada@example.com until I say otherwise.”
search_usersset_user_activeMCP project
“Start an MCP project for my tools server and show me how clients will connect.”
create_mcp_projectget_environment_setupStatus check
“Who am I signed in as, and how many users are in production?”
whoamilist_projectsget_user_count
Tools
Console work, handled by your agent
Each tool maps to something you would otherwise click through in the console.
Projects
List your projects, create one, or start an MCP project, then pull the environment setup for each.
OIDC clients
Create, update, and list clients, and check redirect URIs before a sign-in fails on them.
Users
Search users, count them, and find out why someone is locked out. Suspend or reinstate with one call.
Diagnostics
Run an OIDC configuration test and see what is wrong with discovery, keys, or redirects.
Code snippets
Get the SDK config and environment values for your framework, current to your environment.
Audit
Actions your agent takes are logged with the channel they came through, next to console activity.
Scoped access, no secret keys
Your agent gets only what each call needs
There is no secret key to paste into a config. You sign in, and your agent works within your role.
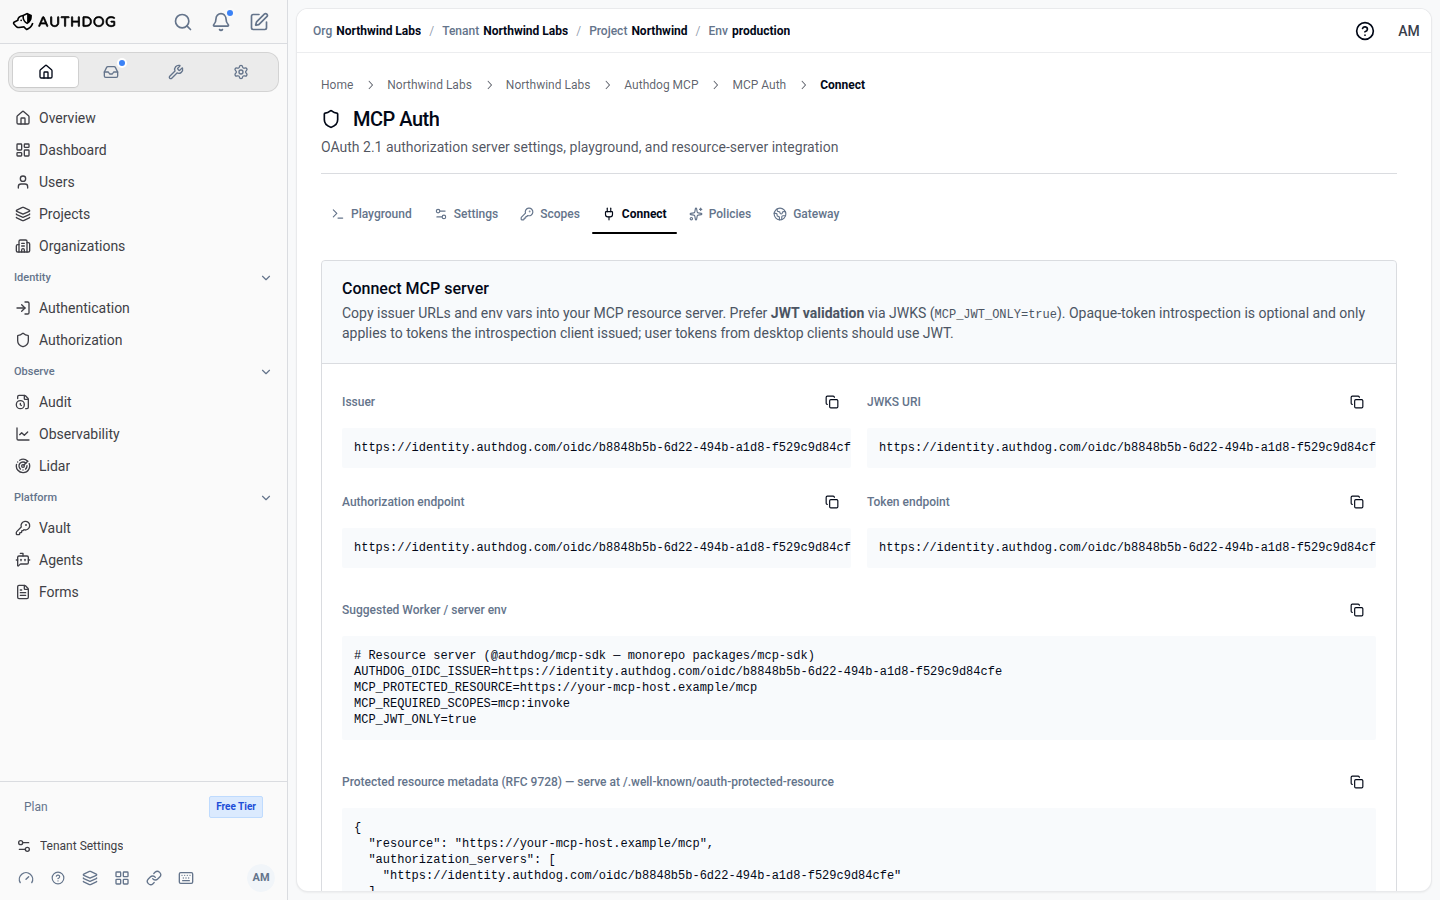
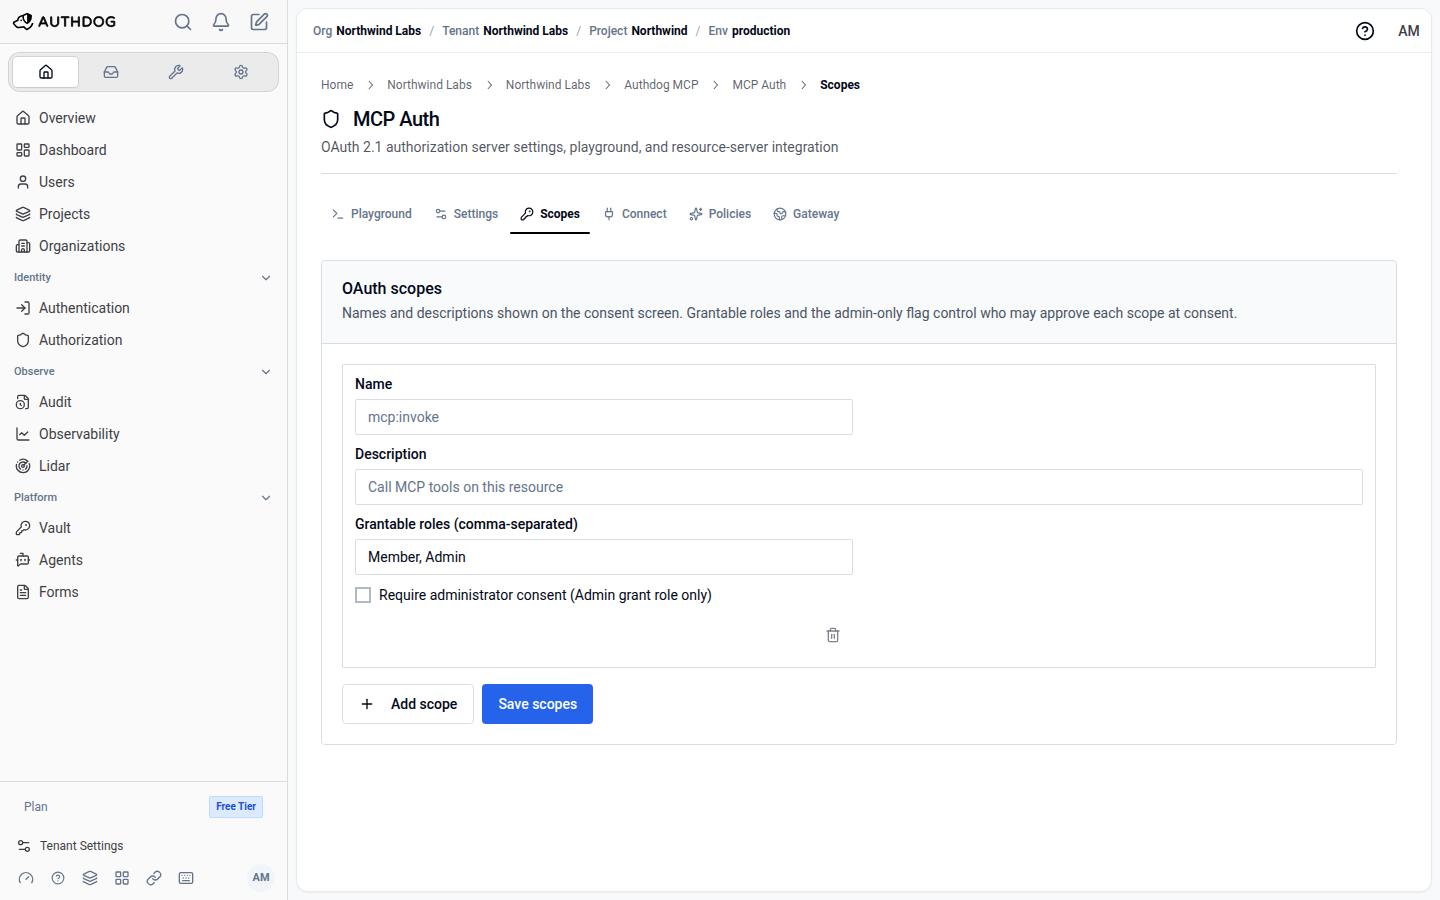
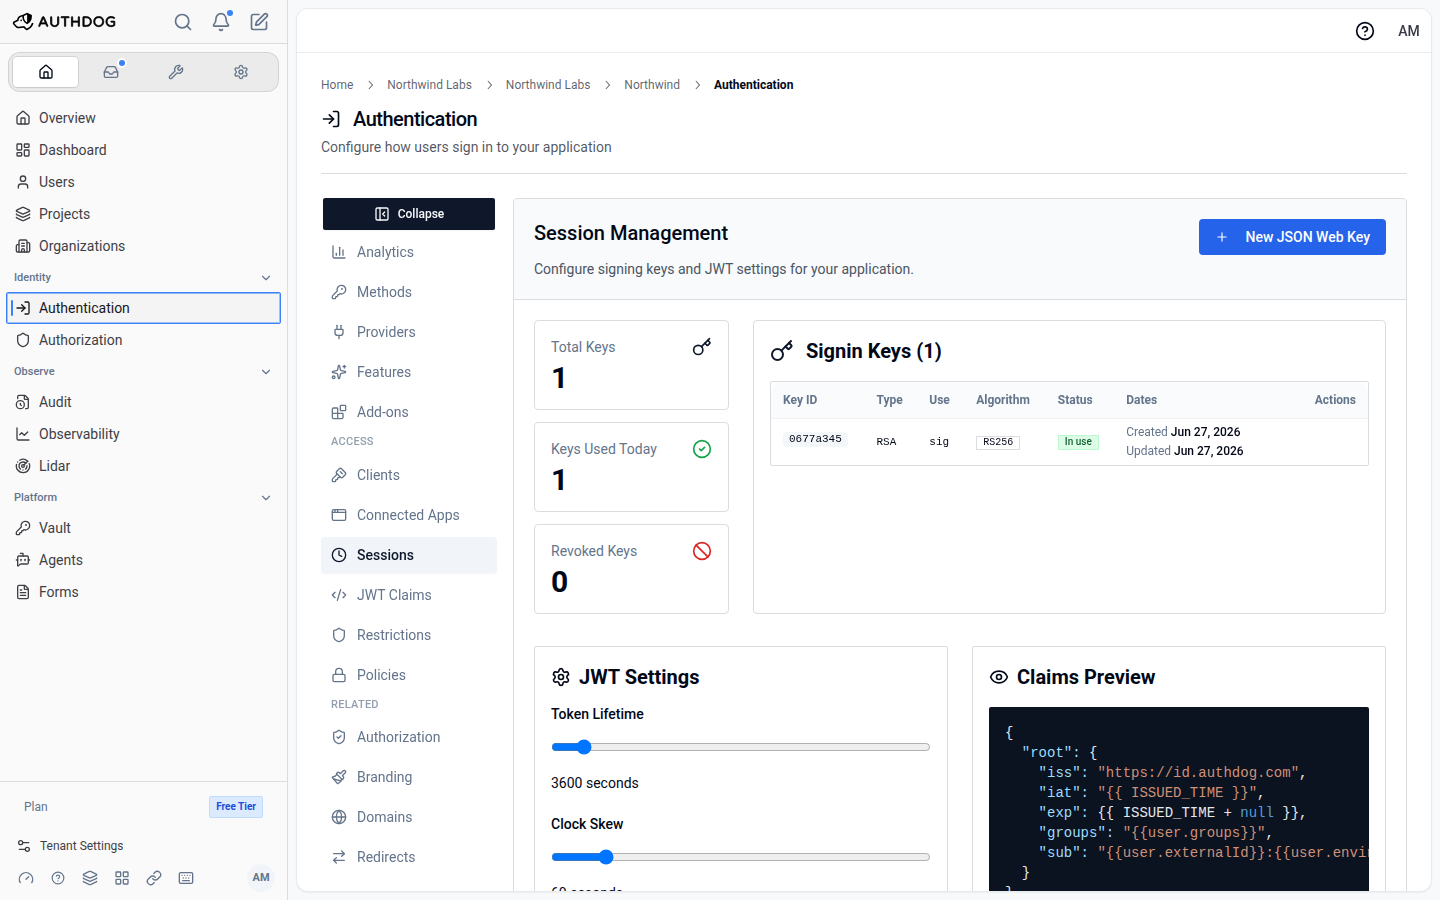
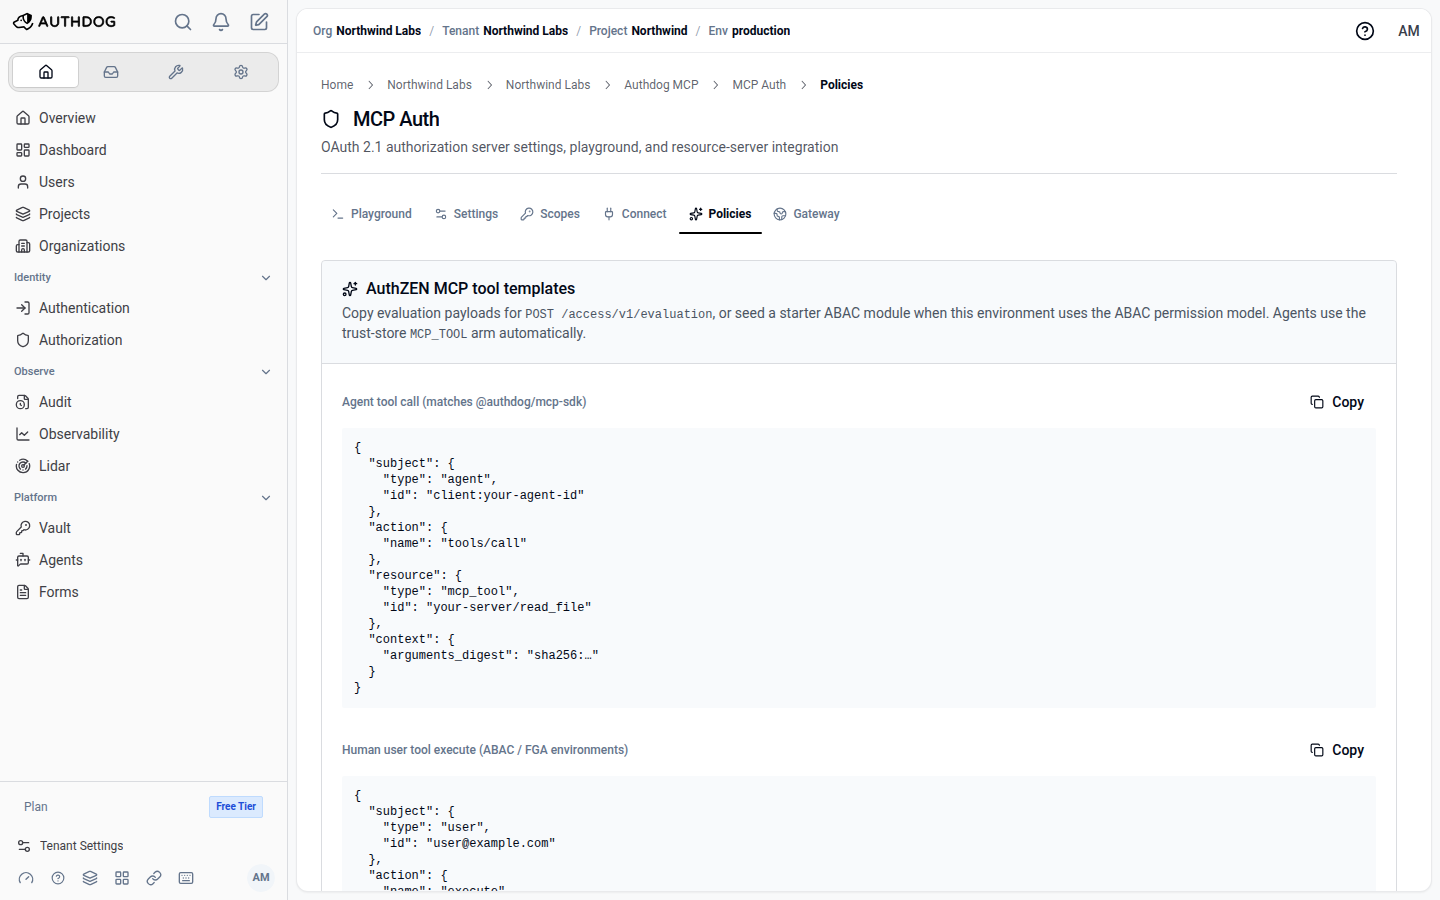
1. Sign in
Your own MCP servers
Put OAuth in front of the servers you build
The same identity layer fronts your MCP servers: register each server, bind an OIDC client, and keep every tool call attributable.
Register a server
How it works
Three steps to production
Connect
Run authdog mcp install, or add https://api.authdog.com/mcp to any MCP client.
Approve
Sign in and approve the scopes your agent asks for.
Ask
Tell your agent what to set up. Every call lands in the audit log.
Free trial
Request a free trial
Tell us what you're building and we'll get you set up with a trial, plus someone who can answer questions as you evaluate.
- Full access to the platform while you evaluate it
- Help wiring it into your stack from someone who knows it
- Answers on SSO, SCIM, residency, and compliance requirements
Run Authdog from your agent
Connect the MCP server, approve the scopes, and let your agent do the dashboard work.